← Portfolio
signet
Configuration and secrets management for Kubernetes, built on SPIFFE workload identity
- Go
- gRPC
- SPIFFE
- Kubernetes
- Postgres
- Helm
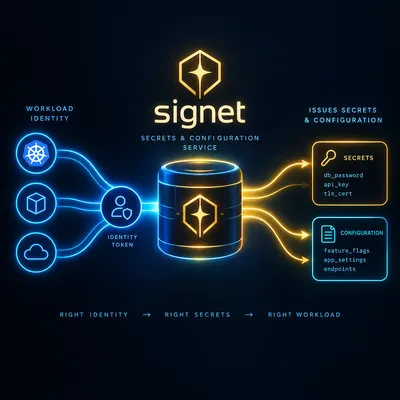
Signet gets the right secrets and configuration to the right workload. A workload proves who it is with its SPIFFE identity rather than a token someone had to hand it, and signet returns only what that identity is allowed to see.
Secrets are kept in git, encrypted with SOPS and age. Signet decrypts them on the server, re-encrypts each one under its own key, and streams changes to the workloads that watch them.
Goals
- Identity, not tokens. Workloads authenticate with SPIFFE/SPIRE, so there is no bootstrap secret to distribute.
- Git is the source of truth. Encrypted secrets and configuration are synced from a repository by webhook and periodic reconciliation.
- Encrypted at rest, layer by layer. Envelope encryption with AES-256-GCM, unsealed by Shamir’s Secret Sharing, an operator key, or a Kubernetes Secret.
- Safe rollouts. gRPC watches push changes, and a distributed restart lock lets workloads restart one at a time when they must.
- Accountable. Every access, permitted or denied, is written to a tamper-evident, HMAC-chained audit log.
Status
Released and in use: authstar takes all of its configuration and secrets from signet. The server is Go; clients are available for Go, Python, Rust, TypeScript, and C#. Signet installs with a Helm chart; see GitHub for instructions.