← Portfolio
authstar
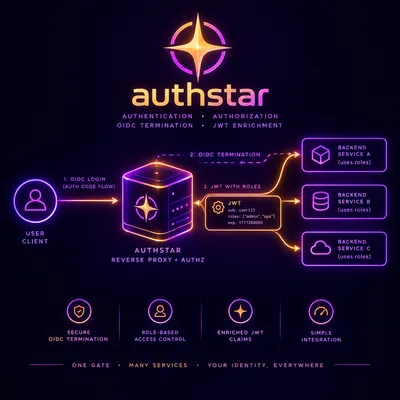
A multi-tenant authentication and authorization platform built around a reverse proxy that terminates OIDC and enriches JWTs with roles
- Rust
- TypeScript
- SvelteKit
- RabbitMQ
- Helm
Authstar puts one gate in front of many services. A reverse proxy handles the OAuth2/OIDC login, issues session and internal JWTs, enriches them with the user’s roles, and forwards each request to the application behind it. Applications check the token with a small client SDK instead of writing their own authentication.
Goals
- One gate, many services. Login, sessions, and role checks live in the proxy, not in every application.
- Enriched tokens. Backend services receive a JWT that already carries the roles they need to authorize a request.
- No static secrets on disk. All configuration and secrets come from signet over SPIFFE mTLS.
- Simple integration. TypeScript SDKs for JWT validation, including a Fastify plugin, keep adoption to a few lines.
Parts
| Part | Role |
|---|---|
| portcullis | The edge proxy and auth engine, in Rust |
| tower | Identity, roles, tenants, and applications |
| keep | Payments and billing through Stripe |
| herald | Templated communications and opt-outs |
| lookout and chronicle | Analytics ingestion over RabbitMQ, and its storage and reporting |
| web and steward | The admin app and hosted pages, and the operator console |
One Helm chart installs every service.
Status
In design and early build. The client SDKs are released; the services are not yet.